

The basics:
- Quest detected unauthorized access to its lab services manager platform Oct. 21
- Patient records may have been accessed; number of people affected remains unknown
- Company paused access to the system, is investigating with cybersecurity experts
Quest Diagnostics disclosed a cybersecurity breach that may have exposed patient records.
In an Oct. 22 regulatory filing, the Secaucus-based testing provider reported that it discovered unauthorized access to its Quanum Lab Services Manager platform the previous day and notified federal law enforcement.
According to Quest, the system allows certain clients to order laboratory tests and access test results.
Quest said it believes certain patient records may have been accessed, but it did not disclose how many individuals may have been affected or specify what information may have been compromised.
A spokesperson for the company referred NJBIZ to an FAQ page posted on its website Oct. 23.
Upon learning of the cyberattack, Quest said it “paused access to the system.” The incident remains under investigation by the company with assistance from external cybersecurity experts, according to Quest.
“Our core business operations are not impacted and remain up and running,” Quest added.
Large client base
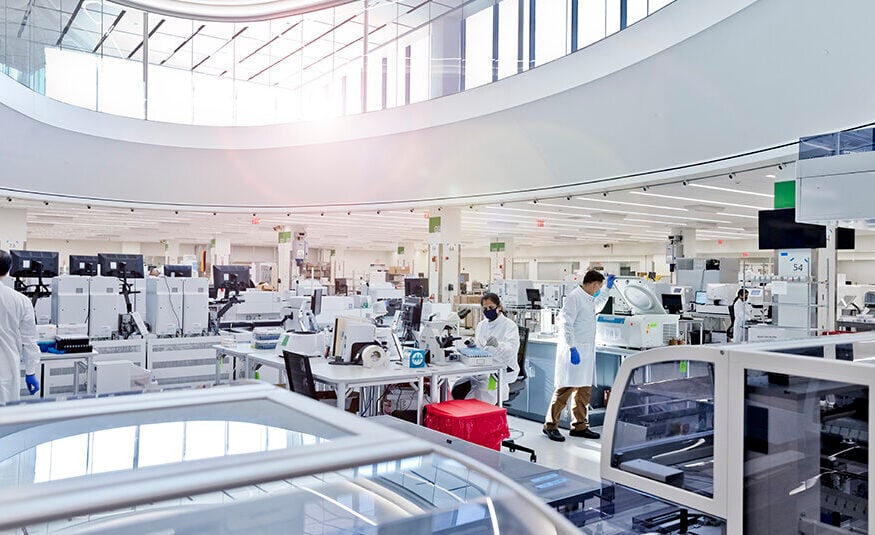
One of the nation’s largest medical laboratory operators, Quest provides diagnostic testing and related services to physicians, hospitals, health plans and patients. Its test offerings – which range from routine bloodwork to specialized screening for cancer and other diseases – are available to more than 90% of U.S. insured lives, the company says.
The company serves approximately one-third of American adults annually through its 7,770-plus patient access points across North America. It also handles testing for half of the physicians and hospitals in the U.S. each year.
Quest’s workforce of 57,000 employees includes a medical and scientific staff of over 700 physicians, according to its website.
Previous attacks
This isn’t Quest’s first breach, The Associated Press noted.
In 2016, the company said lab results and contact information for about 34,000 people were exposed in an online breach. During a 2019 incident involving a third-party billing provider, the personal information associated with approximately 11.9 million Quest patients was compromised, the outlet reported.
Fierce Biotech noted that Quest’s latest breach adds to a growing number of cyberattacks on the healthcare sector. Other recent cyberattacks include medical device makers Abbott, Stryker, Medtronic and Boston Scientific.
Beyond healthcare, sectors such are retail grocery, education technology and utilities are increasingly facing similar threats, according to the AP.
Quest confirmed to the news outlet that its latest breach was unrelated to a separate PHP software vulnerability disclosed earlier this week that prompted companies worldwide to rush security updates.
The post Quest Diagnostics reports patient data breach appeared first on NJBIZ.
